Quick Summary
Residential proxies use legitimate home and mobile internet connections, making malicious traffic harder to detect. Research covering 170 million IP addresses reveals rapid turnover and extensive sharing across providers, challenging traditional IP reputation systems.
Effective security requires looking beyond static IP labels and considering the recency, frequency, and persistence of activity. This context helps detect abuse, reduce false positives, and protect legitimate users.
Introduction
A familiar question in security investigations is often: what can an IP tell us?
For years, that question has had fairly predictable answers. Is the address associated with hosting infrastructure a VPN? Tor? A corporate network? This type of network context becomes an important signal in countless fraud detection systems, access policies, and security investigations.
Residential proxies complicate that equation.
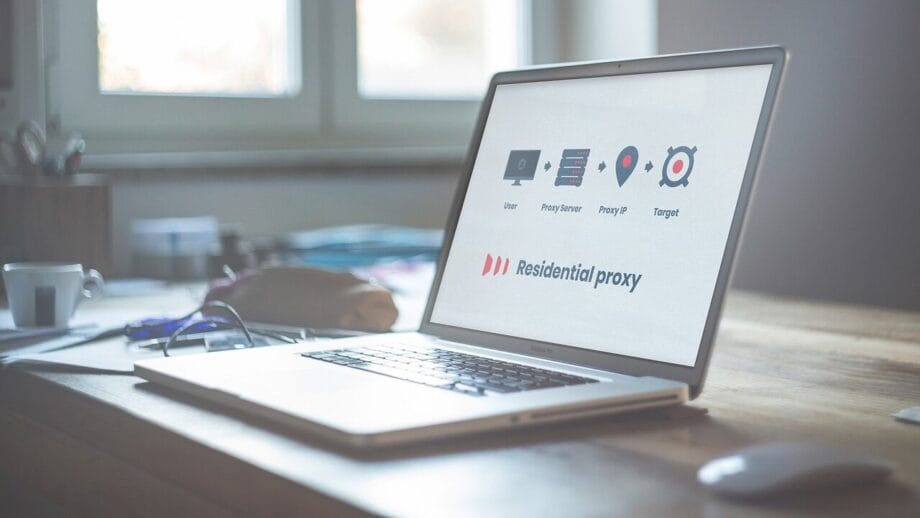
Unlike traditional VPNs or datacenter proxies, residential proxies route traffic through ordinary consumer internet connections. Requests can originate from legitimate broadband providers and mobile carriers, often carrying all the characteristics of ordinary residential traffic. The infrastructure looks familiar, even when the activity behind it isn’t.
For defenders, that creates a more complicated challenge than simply identifying whether an IP address has been associated with a proxy service. It requires understanding how residential proxy infrastructure behaves, including how it rotates, how long it stays active, and how extensively the same infrastructure is shared across different proxy networks.
Over 90 days, our research team analyzed more than 170 million residential proxy IP addresses collected through direct observation of commercial residential proxy networks. What emerged was an ecosystem that behaves very differently from the assumptions traditional IP reputation models depend on.
The implication reaches well beyond residential proxies themselves. As more internet infrastructure becomes dynamic, shared, and continuously reassigned, static reputation becomes a weaker predictor of future behavior. Understanding an IP increasingly depends less on what has been seen before and more on how recently and consistently it has been observed.
Residential Proxies are Built on Legitimate-Looking Infrastructure
Traditional VPN services typically operate their own servers or lease infrastructure from cloud providers. Their traffic often originates from recognizable hosting networks, making infrastructure-level classification comparatively straightforward.
Residential proxies take a different approach.
Commercial providers obtain access to real residential internet connections. Sometimes they’re through voluntary participation; sometimes they’re routed through compromised devices. They then resell that connectivity to customers who want their traffic to appear as ordinary consumer traffic.
From a website or security team’s perspective, a request might appear to originate from a broadband subscriber in Chicago, a fiber customer in Paris, or a mobile subscriber in São Paulo. The underlying IP address visible may genuinely belong to a legitimate ISP and consumer connection. The user or system initiating the request, however, may be somewhere entirely different.
That distinction explains why residential proxies have become increasingly common in abuse. Traffic can blend into the same consumer networks used by genuine customers, making the simple distinction between “residential” and “suspicious” increasingly unreliable. Residential proxy infrastructure is now used across activities such as credential stuffing, account creation, scraping, advertising fraud, and payment abuse. The traffic blends into the same networks used by legitimate customers.
Stability in Reputation Systems is Disappearing
Much of today’s IP reputation ecosystem was built around the idea that an IP address accumulates a reputation over time. An address previously associated with malicious or suspicious activity can signal risk in future decisions. An address with a long history of legitimate activity becomes more trustworthy. Over time, those observations help inform automated decisions.
The utility of historical records relies on persistent behavior. Residential proxy infrastructure fundamentally challenges that utility.
Across more than 170 million residential proxy IP addresses observed over 90 days, we found that approximately 60% appeared only once during the entire observation window.
Even among addresses that persisted longer, turnover remained constant. Average IP visibility was just 4.56 days, and only 9% of IPs were reobserved within 7 days.
For defenders, this means yesterday’s observations often tell only part of today’s story.
An IP address with no previous residential proxy history may simply have entered a provider’s pool this morning. Equally, an address observed as a proxy may later return to residential use.
Infrastructure Sharing is Common
One of the most striking findings from our research was how extensively residential proxy providers shared infrastructure.
46% of observed residential proxy IPs appeared simultaneously across multiple commercial provider networks. In some cases, a single IP address appeared in 101 different residential proxy services over the course of our observations.
Several mechanisms can create this overlap. Providers frequently source connectivity from overlapping partner networks, software distribution channels, or aggregation services. Multiple companies may advertise independent proxy offerings. As a result, services marketed as separate proxy networks can share the same underlying residential IP infrastructure.
For security teams, this makes provider-level attribution significantly more complicated. Blocking one provider does little to address the broader ecosystem if the same infrastructure remains available through dozens of others. Likewise, attributing activity to a particular commercial provider becomes increasingly difficult when multiple services expose the same residential connection at the same time.
The infrastructure has become far more interconnected than individual provider marketing might suggest. Commercial providers that appear independent at the brand level can be substantially interconnected at the infrastructure level.
Binary Classifications Leave Out Valuable Context
Security flags often only indicate whether an IP address is a residential proxy. That binary answer only goes so far.
Consider two residential proxy IPs.
One was observed once for a few minutes and has never been observed again. The other has been consistently observed across multiple commercial proxy providers for months.
A binary flag treats both observations similarly. Their histories tell a more nuanced story. Treating those observations as equivalent misses important context.
Recency, frequency, and persistence provide additional context about the strength and relevance of a residential proxy observation. That context helps analysts understand how an address is behaving today, rather than relying exclusively on historical labels.
For security teams, this context reduces unnecessary investigation time. Analysts can better distinguish between isolated historical observation and sustained proxy activity.
Rather than replacing existing detection logic, context about recency, frequency, and persistence helps prioritize risk decisions that would otherwise rely on binary flags.
Residential Proxies Illustrate a Broader Shift
Residential proxies represent a larger challenge happening across internet infrastructure. The relationship between an IP address and the network behind it is not always static.
IP addresses increasingly move between organizations. Networks are continuously reassigned. Hosting providers expand into residential services. Mobile gateways serve millions of users through relatively small address pools. IPv6 continues to reshape assumptions about address ownership and persistence.
Fresh observations increasingly matter as much as historical records. Evidence of how infrastructure is behaving over time complements ownership records. Multiple independent signals together provide a stronger understanding than any single classification can offer.
Looking Beyond Reputation
Residential proxies are now an established part of internet infrastructure, supporting both legitimate commercial applications and abuse activity. That means defenders face a balancing act.
Blocking every residential proxy creates unnecessary friction for legitimate users, researchers, businesses, and consumers whose traffic happens to share similar infrastructure. Ignoring residential proxies altogether leaves organizations exposed to credential attacks, scraping, fake account creation, and payment fraud.
Neither extreme reflects how much an IP address can tell us.
An IP address is not always simply “good” or “bad.” Its value as a security signal depends on context. How recently has it been observed? Has its behavior remained stable? How persistently? Across how many providers? As internet infrastructure grows more dynamic, those contextual questions become increasingly valuable.
Residential proxies are not simply another category of anonymization service. They show how internet infrastructure is evolving: shared, constantly changing, and often behaving in ways static records struggle to capture.
The organizations that adapt most successfully will move beyond treating IP addresses as fixed identities and start understanding them as continuously changing signals. That shift doesn’t just improve residential proxy detection. It leads to better security decisions across every workflow that involves an IP address.


